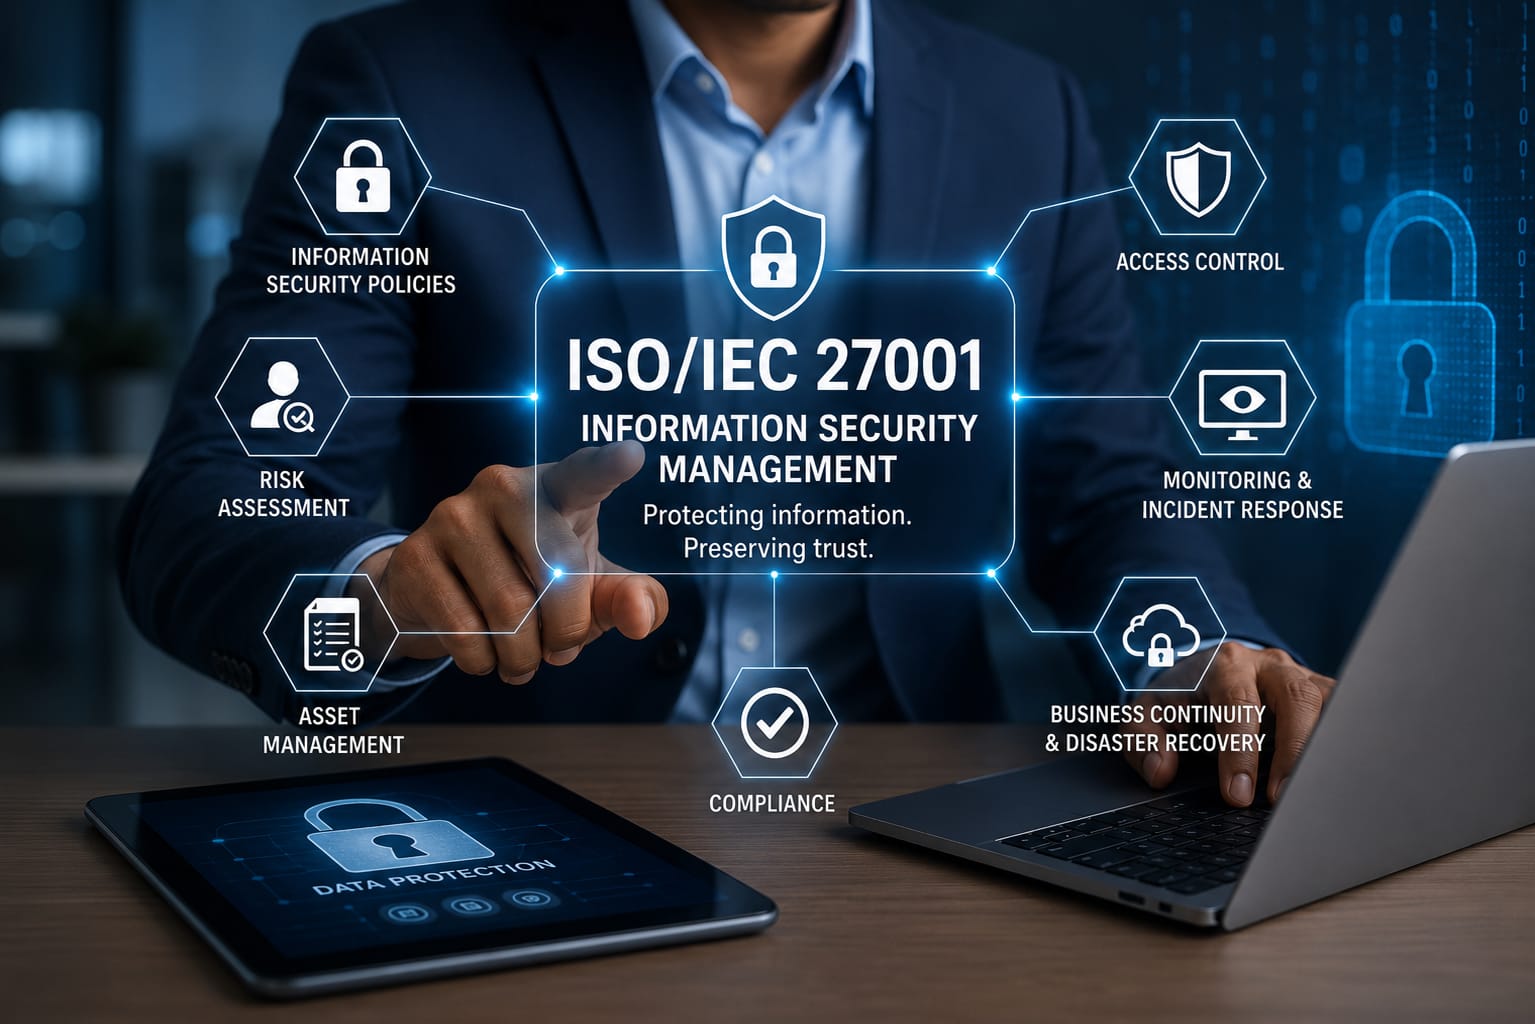
ISO/IEC 27001 Information Management Systems Lead Auditor Training Course eLearning (PECB)

About Course

The ISO/IEC 27001 Information Security Management System (ISMS) Lead Auditor Training Course – PECB eLearning is a flexible, self-paced programme designed to equip participants with the knowledge and competencies required to audit Information Security Management Systems in accordance with ISO/IEC 27001:2022 and ISO 19011 audit guidelines.

This course provides a comprehensive understanding of information security principles, audit methodologies, and risk-based auditing approaches. It focuses on enabling learners to plan, conduct, report, and follow up on ISMS audits while ensuring the confidentiality, integrity, and availability of information assets.

Delivered through the PECB online learning platform, the course allows participants to study at their own pace while gaining practical knowledge through case studies, interactive content, and real-world audit scenarios. It also prepares learners for the PECB ISO/IEC 27001 Lead Auditor certification examination.

Show More

What Will You Learn?

  • Understand ISO/IEC 27001:2022 requirements and ISMS principles.
  • Apply ISO 19011 audit guidelines in audit practice.
  • Plan, conduct, and manage ISO 27001 audits effectively.
  • Evaluate information security risks and controls.
  • Identify and report nonconformities.
  • Lead or support ISMS audit teams.
  • Strengthen organizational information security posture.
  • Apply risk-based auditing techniques.
  • Understand certification and compliance processes.
  • Prepare for PECB ISO 27001 Lead Auditor certification.

Course Content

Introduction to Information Security and ISO 27001
Fundamentals of information security CIA triad (Confidentiality, Integrity, Availability) Overview of ISO/IEC 27001:2022 Importance of ISMS in organizations

ISO 27001 Framework and Structure
Structure and clauses of ISO 27001 Risk-based thinking in ISMS Integration with other management systems (ISO 9001, ISO 42001, etc.) Organizational context and leadership

Information Security Risk Management
Risk identification and assessment Threats, vulnerabilities, and impacts Risk treatment and Statement of Applicability (SoA)

ISO 27001 Annex A Controls
Security control categories Access control and identity management Cryptography and data protection Incident management and security monitoring

Audit Principles and ISO 19011 Guidelines
Audit principles and ethics Audit programme management Audit planning and preparation Evidence collection and sampling technique

Conducting ISMS Audits
Opening and closing audit activities Interviewing and evidence gathering techniques Nonconformity identification and classification Audit documentation and reporting

Lead Auditor Roles and Responsibilities
Managing audit teams Communication with auditees Audit leadership and coordination Professional ethics and conduct

ISMS Performance Evaluation
Monitoring and measurement of ISMS Internal audit and management review Key performance indicators (KPIs) Continuous improvement processes

Certification and Compliance Process
Certification audit stages (Stage 1 & Stage 2) Surveillance and recertification audits Compliance obligations Common audit findings

Exam Preparation and Case Studies
Practical audit scenarios Mock audit exercises Common mistakes in ISO 27001 audits Preparation for PECB certification exam

Student Ratings & Reviews
No Review Yet
No Review Yet